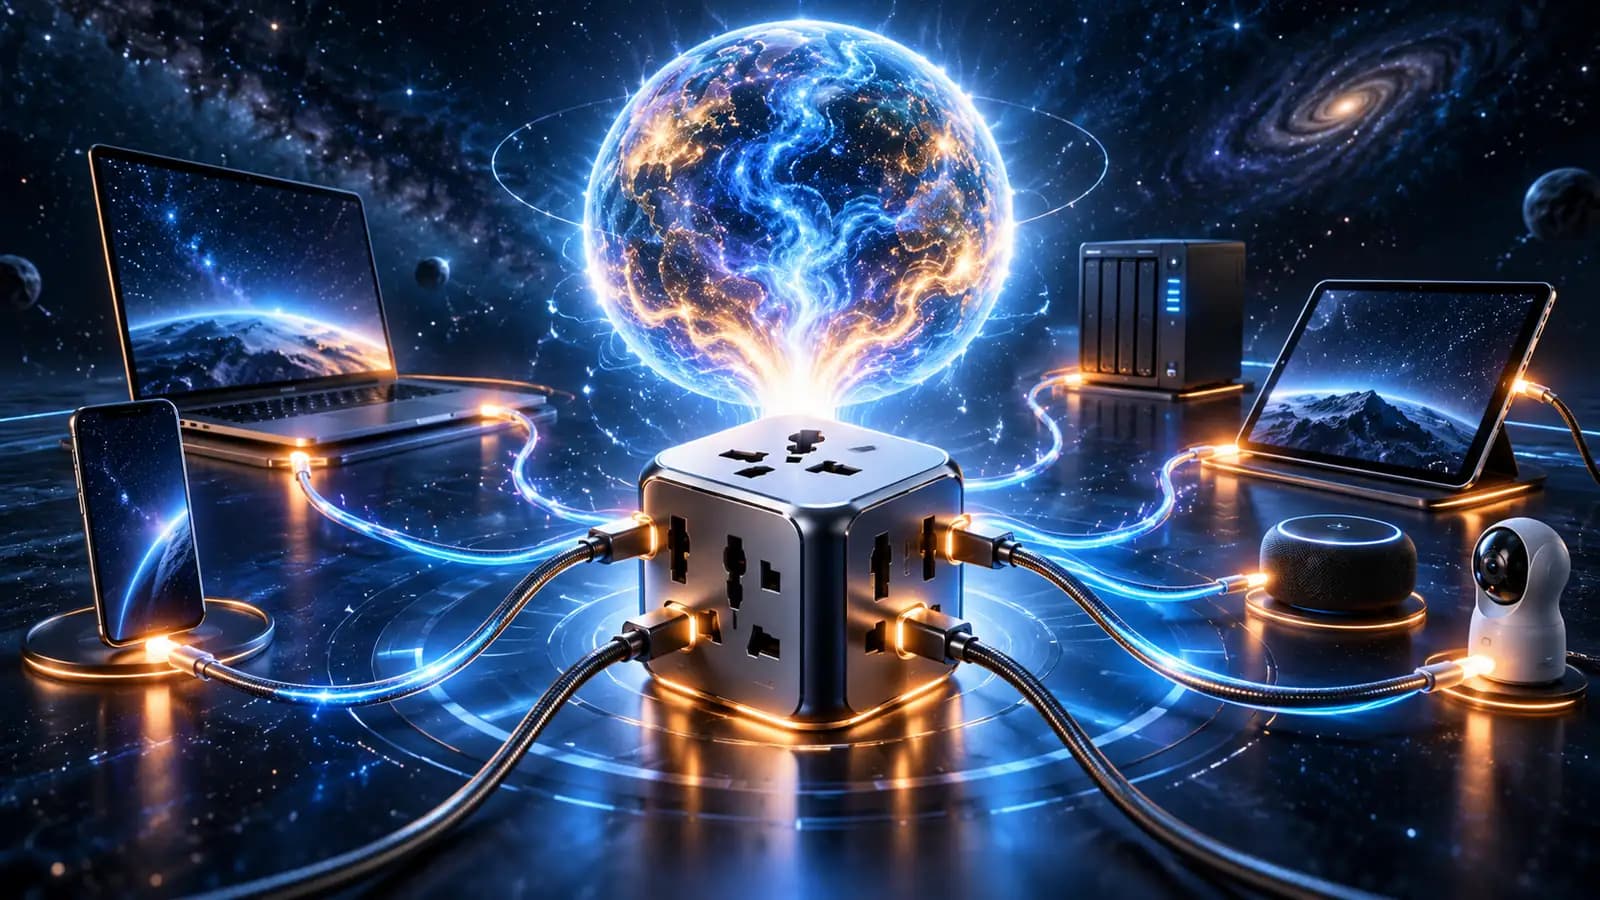
The Model Context Protocol (MCP) is an open standard that defines how AI applications access tools and data, so that not every connection has to be built individually. Its developers often use the image of a USB-C port: one plug, many devices. For businesses this means AI tools can be connected to calendar, customer management or documents, but also that new security questions arise.
What is MCP and which problem does it solve?
A language model knows only what is in its training and in your request. To be useful in daily work it has to reach your calendar, your documents or your CRM. In the past, each combination of AI application and tool needed its own connection. MCP replaces this with a shared standard: a tool provides an MCP server once, and every supporting AI application can use it. Anthropic introduced the standard in November 2024; the specification and documentation are maintained by the community at modelcontextprotocol.io.
Individual systems talk through interfaces, as explained in What is an API?. MCP sits on top of these and standardises how AI applications use them.
How is MCP structured?
MCP has three roles. The host is the AI application, such as a chat program or a development tool. Inside it runs a client that maintains the connection. The server offers capabilities. Servers can run locally on your computer or remotely over the internet.
| Term | Meaning | Example |
|---|---|---|
| Host | The AI application you work with | Chat program, editor |
| Client | Connection part inside the host, talks to one server | Managed by the host |
| Server | Provides tools, data and templates | Calendar server, document server |
| Tool | An action the model can call | Create appointment, find contact |
| Resource | Data the model can read | File, database entry |
After your request, a model decides which tool to call. How such models, as agents, carry out several steps on their own is described in What is agentic AI?.
Which security questions should you ask?
Every MCP connection gives an AI application access to your systems. Treat it like a new employee with a bunch of keys. Before use, ask these questions:
- Who runs the server, and where does the software come from?
- What rights does it have: read only, or also write and delete?
- Which data leaves your premises, and where does it go (model provider, servers)?
- How does sign-in work, and can rights be limited per user?
- Are write actions tied to approval by a person?
- Are there logs of what was executed and when?
Two risks deserve particular attention. First, third-party code: a downloaded server runs with your rights and should come from a trustworthy source. Second, prompt injection: if a server returns content from emails or web pages, hidden instructions may sit in it that lead the model to unwanted actions. The OWASP project on LLM risks describes this in more detail.
When is MCP worthwhile for a small business?
MCP is worthwhile when an AI tool is meant to access several of your systems regularly, for example to match enquiries with customer data or suggest appointments. You do not need it for occasional text tasks in a chat. An overview of agents in business is in What is an AI agent?.
- Benefit named: which task gets better through the access?
- Origin and operator of the MCP server checked
- Permissions limited to the essentials, read-only at first
- Data flow and data protection terms clarified
- Approval set up for write actions
- Logs enabled and reviewed in the first weeks
Conclusion: a standard that demands care
MCP makes it easier to connect AI tools to your systems, and it demands the same scrutiny of rights and data as any other interface. If you want to check which connections are sensible and safe in your business, see our AI automation service or describe your process.